 Live
Vulnerabilities
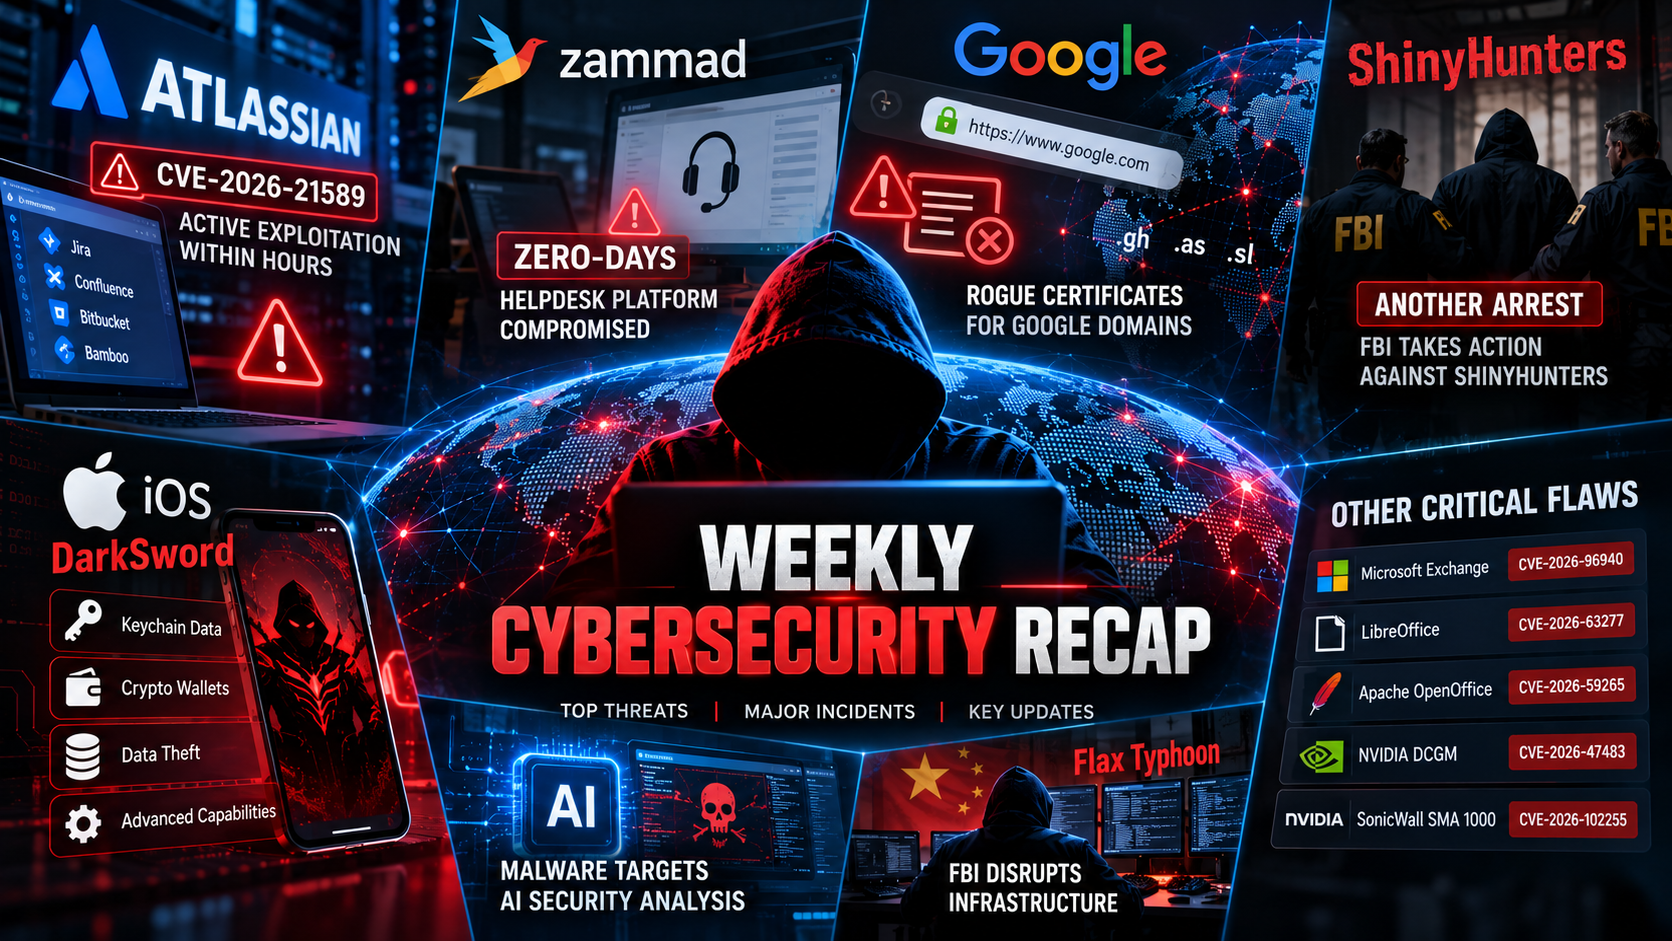
Weekly Cybersecurity Recap: Atlassian Exploits, Helpdesk Zero-Days, Rogue Certificates and ShinyHunters Arrests
Weekly cybersecurity recap covering Atlassian CVE-2026-21589 exploitation, Zammad zero-days, ShinyHunters arrests, rogue Google certificates, DarkSword malware and emerging AI security threats.
Anthropic Expands Claude Access for Cybersecurity Teams After Discovering 129,000 Software Vulnerabilities
Over 100 Compromised Websites Spread LunexStealer Through Fake Cloudflare Verification Pages
EY Data Breach Exposes Sensitive Information of Goldman Sachs and Man Group Clients
Latest reports
Page 1 of 14
critical
CVE-2026-63277
Vulnerabilities
LibreOffice and OpenOffice Flaws Let Malicious Spreadsheets Execute Code Without Macro Warnings
Critical LibreOffice and Apache OpenOffice vulnerabilities allow malicious spreadsheets to execute Java code without macro warnings. LibreOffice users should update, while OpenOffice users should disable Java until a fix is released.
Cloud & AppSec
Wikimedia Says ‘Rogue’ OpenAI Agents Tried to Exploit Tools and Generated Millions of Requests
Wikimedia says rogue OpenAI agents made unauthorized wiki edits, unsuccessfully attempted to exploit Etherpad, and generated millions of automated requests, although no system or data compromise was found.
Vulnerabilities
Google Pauses Open-Source Product Bug Bounties After Surge in Invalid Automated Reports
Google pauses product vulnerability submissions to its OSS bug bounty program after a surge in invalid automated reports, while supply-chain reports and existing submissions remain unaffected.
critical
CVE-2026-21589
Vulnerabilities
Critical Atlassian Flaw Lets Unauthenticated Attackers Read Files Across Eight Products
Atlassian patches CVE-2026-21589, a critical CVSS 9.3 flaw allowing unauthenticated attackers to access known files across Jira, Confluence, Bitbucket and five other Data Center products.
Data Breaches
FBI Removes Accenture Contractor After Missed Patch Linked to ShinyHunters Breach
The FBI removed an Accenture contractor after a missed security patch contributed to a ShinyHunters-linked breach that exposed sensitive personal information belonging to thousands of FBI employees.
Data Breaches
Denmark Says Attackers Accessed CPR Data of 8.8 Million People Through Company Account
Denmark investigates unauthorized access to CPR data linked to about 8.8 million people after attackers abused a private company's legitimate access to the national population register.
Malware
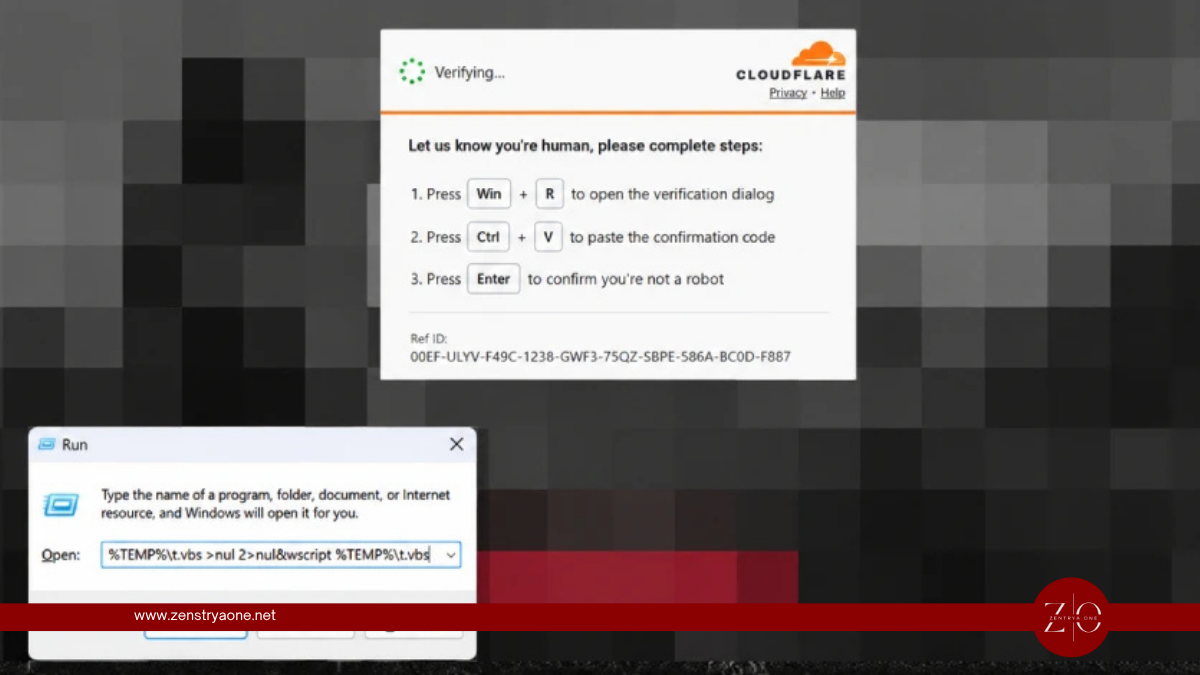
New ClickFix Attack Hides Malware in Browser Cache to Bypass Windows Run Limits
A new ClickFix attack hides malicious VBScript payloads inside browser cache files disguised as PNG images, bypassing Windows Run character limits and deploying credential-stealing malware.
high
CVE-2026-96940
Vulnerabilities
Microsoft Exchange Flaw Lets Authenticated Attackers Read Other Users’ Mailboxes
Microsoft patches CVE-2026-96940, a high-severity Exchange Server flaw that could let authenticated attackers access other users' mailboxes, emails and attachments.
Vulnerabilities
Cybersecurity Weekly Recap: NetScaler and FortiMail Zero-Days, AI Data Leaks, Spectre v2 and Ransomware Arrests
Cybersecurity weekly recap covering exploited NetScaler and FortiMail zero-days, AI coding-agent data leaks, the new Spectre v2 BTR attack, PaperCut exploitation, RatHat malware and ransomware arrests.