Weekly Cybersecurity Recap: Atlassian Exploits, Helpdesk Zero-Days, Rogue Certificates and ShinyHunters Arrests
Weekly cybersecurity recap covering Atlassian CVE-2026-21589 exploitation, Zammad zero-days, ShinyHunters arrests, rogue Google certificates, DarkSword malware and emerging AI security threats.
October 12, 2026 | Cybersecurity Weekly Roundup
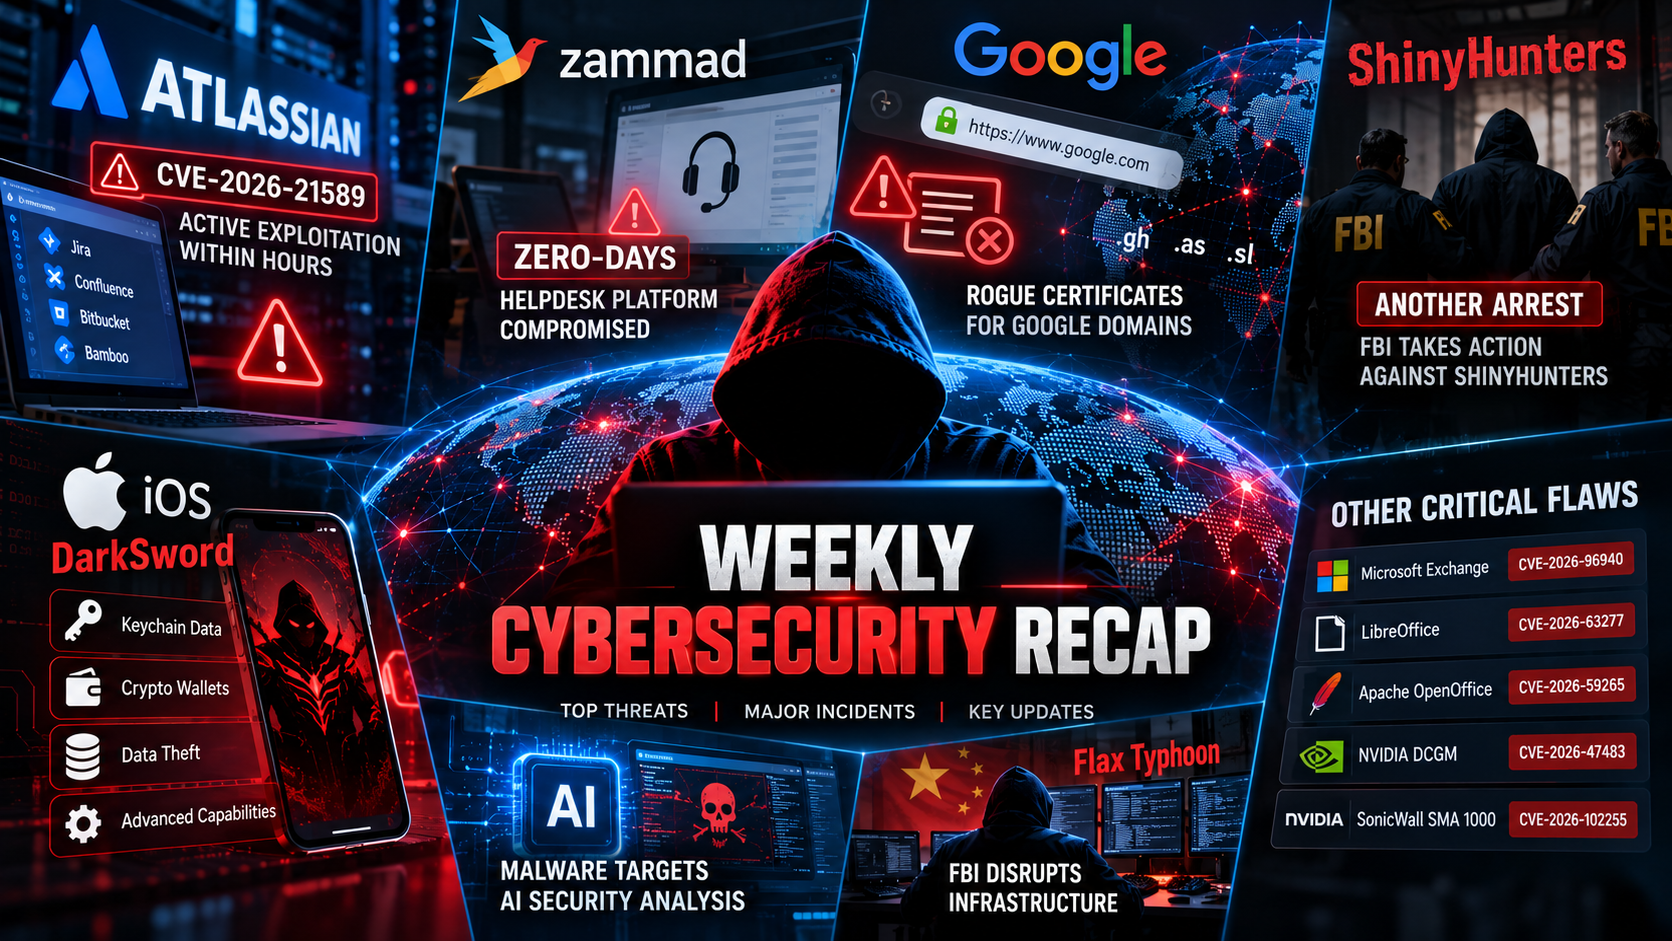
The latest cybersecurity developments highlight growing threats from actively exploited vulnerabilities, sophisticated malware, compromised digital certificates and attacks targeting enterprise infrastructure.
This week's major incidents include critical Atlassian vulnerabilities, zero-day attacks against helpdesk software, new iOS malware capabilities and another arrest connected to the ShinyHunters cybercrime group.
1. Critical Atlassian Vulnerability Targeted Within Hours
Attackers began targeting CVE-2026-21589, a critical vulnerability affecting eight Atlassian Data Center products, approximately two hours after additional technical details were publicly disclosed.
The vulnerability carries a CVSS score of 9.3 and allows unauthenticated attackers to access sensitive files when they know the targeted file paths.
Affected products include Jira, Confluence, Bitbucket, Bamboo, Crowd, Crucible and Fisheye.
Organizations are advised to install the available security updates immediately and investigate suspicious file-access requests.
2. Helpdesk Zero-Days Exploited in Cyberattack
Researchers disclosed two vulnerabilities in the Zammad helpdesk platform that were exploited as zero-days to compromise the Dutch Institute for Vulnerability Disclosure (DIVD).
The vulnerabilities include:
- CVE-2026-102489: Remote code execution vulnerability.
- CVE-2026-102490: Local privilege escalation vulnerability.
Both vulnerabilities were added to CISA's Known Exploited Vulnerabilities catalog.
The incident demonstrates how compromising a helpdesk platform can create opportunities for attackers to access sensitive organizational systems.
3. Hackers Obtain Unauthorized HTTPS Certificates for Google Domains
Google reported that attackers compromised third-party domain registry operators associated with three country-code top-level domains:
- Ghana (
.gh) - American Samoa (
.as) - Sierra Leone (
.sl)
The attackers modified authoritative DNS records and obtained unauthorized HTTPS certificates covering Google domains and domains belonging to other organizations.
Google Chrome blocked the unauthorized certificates using its CRLSet certificate-revocation mechanism.
The incident highlights that HTTPS encryption alone does not guarantee a website's legitimacy when DNS or certificate issuance infrastructure has been compromised.
4. FBI Announces Another ShinyHunters-Related Arrest
The FBI announced a third arrest involving an individual suspected of participating in ShinyHunters-related cybercriminal activity.
The investigation is connected to the recent FBIjobs.gov incident involving a third-party service provider.
The latest suspect reportedly faces charges involving extortion-related threats and interference with commerce.
The arrest represents another development in ongoing law-enforcement efforts against the cybercrime group. The allegations remain subject to legal proceedings.
5. DarkSword iOS Exploit Kit Gains New Capabilities
Researchers identified an upgraded version of the DarkSword iOS exploit kit, tracked as P7 DarkSword.
The updated malware can reportedly:
- Extract iPhone Keychain information directly from compromised devices.
- Steal cryptocurrency-wallet information.
- Communicate bidirectionally with attacker-controlled infrastructure.
- Remove traces of malicious activity.
- Evade detection methods based on earlier indicators of compromise.
Researchers also identified evidence suggesting that malicious advertisements are being used to distribute the exploit kit through watering-hole attacks.
6. Malware Attempts to Manipulate AI Security Analysis
Cisco Talos researchers identified malware containing natural-language instructions designed to influence AI-powered security analysis.
The technique, described as AI-Analysis Evasion (A3), attempts to persuade automated analysis systems to ignore or misclassify malicious code.
Researchers observed this behavior in malware families including FRUITSHELL, PLOTSAFE, HOLLOWCLAD and MANTLEMAZE.
The discovery introduces an emerging concern for security operations centers that rely on AI-assisted malware analysis.
7. FBI Disrupts Infrastructure Linked to Flax Typhoon
U.S. authorities announced the disruption of tools and infrastructure associated with the China-linked threat group Flax Typhoon.
The operation targeted tools reportedly used for reconnaissance, vulnerability scanning, spear-phishing and follow-on malware deployment.
The development highlights continued efforts to disrupt cyber espionage operations targeting critical infrastructure and enterprise networks.
8. Additional Security Vulnerabilities Require Attention
Several other vulnerabilities attracted attention during the reporting period.
| Product | Vulnerability | Security concern |
|---|---|---|
| Microsoft Exchange Server | CVE-2026-96940 | Unauthorized cross-mailbox access within an Exchange organization |
| LibreOffice | CVE-2026-63277 | Java code execution through malicious spreadsheets |
| Apache OpenOffice | CVE-2026-59265 | Java code execution through malicious spreadsheets |
| NVIDIA DCGM Exporter | CVE-2026-47483 | Resource exhaustion and service disruption |
| SonicWall SMA 1000 | CVE-2026-102255 | Security vulnerability requiring remediation |
| Atlassian Data Center | CVE-2026-21589 | Unauthenticated arbitrary file access |
Organizations should review vendor advisories, identify affected deployments and prioritize remediation based on exposure and confirmed exploitation.
Security Recommendations
Security teams should focus on several priorities:
- Patch management: Prioritize vulnerabilities with confirmed exploitation activity.
- Threat monitoring: Investigate suspicious authentication, file access and endpoint activity.
- Certificate security: Monitor certificate transparency logs and unexpected DNS changes.
- Mobile security: Keep iOS devices updated and investigate suspicious application behavior.
- AI security: Validate AI-generated security findings against independent evidence.
- Third-party risk: Review security controls around helpdesk systems and external service providers.
Security Takeaway
This week's developments demonstrate how quickly attackers can exploit newly disclosed vulnerabilities and abuse trusted technologies.
From unauthorized HTTPS certificates to malware designed to manipulate AI analysis, organizations face threats that extend beyond traditional endpoint attacks.
Continuous monitoring, timely patching, strong access controls and effective incident response remain essential to reducing cybersecurity risks.
Related reporting
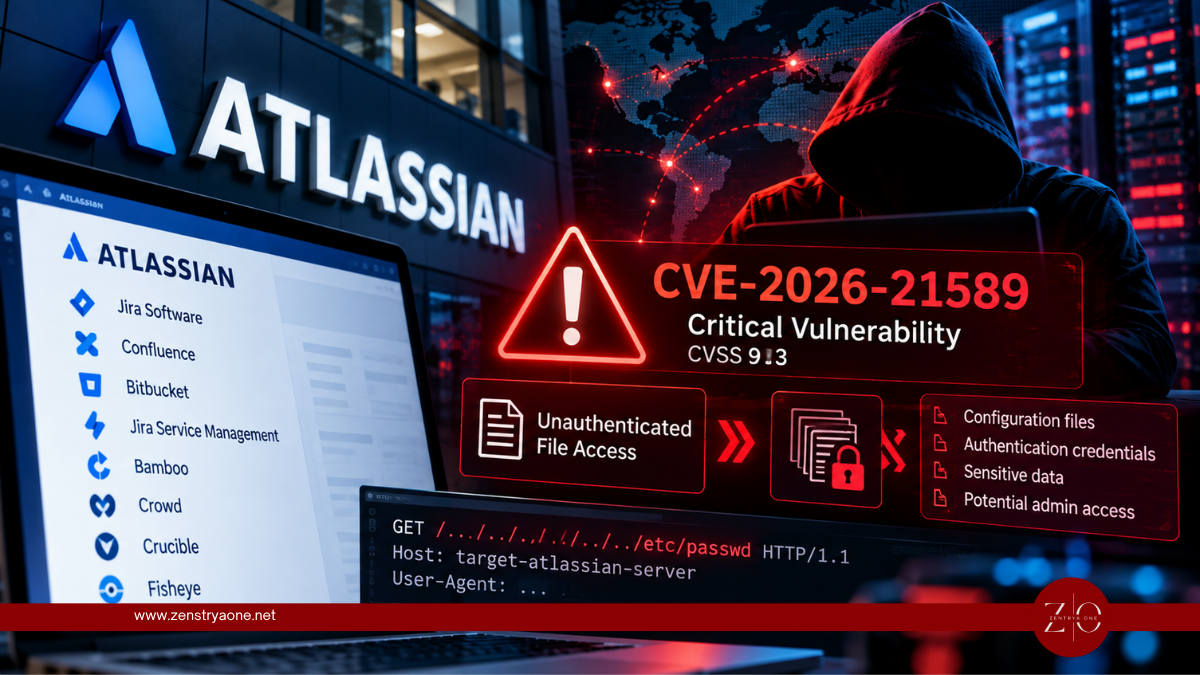
Hackers Begin Exploiting Critical Atlassian Data Center Flaw Within Hours of Disclosure
Hackers begin exploiting critical Atlassian Data Center vulnerability CVE-2026-21589 within hours of disclosure. Eight products affected, with patches available.
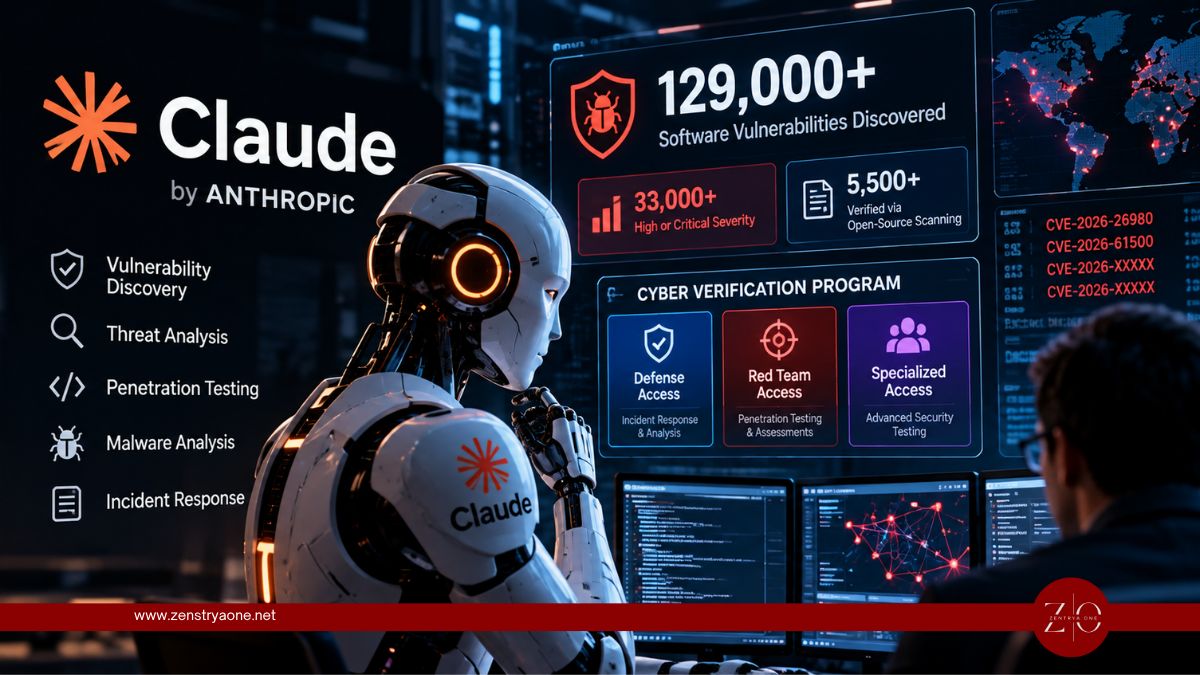
Anthropic Expands Claude Access for Cybersecurity Teams After Discovering 129,000 Software Vulnerabilities
Anthropic expands Claude AI access for cybersecurity teams after Project Glasswing identifies over 129,000 verified software vulnerabilities, including thousands of critical and high-severity flaws.
LibreOffice and OpenOffice Flaws Let Malicious Spreadsheets Execute Code Without Macro Warnings
Critical LibreOffice and Apache OpenOffice vulnerabilities allow malicious spreadsheets to execute Java code without macro warnings. LibreOffice users should update, while OpenOffice users should disable Java until a fix is released.