Critical Next.js ImageResponse Flaw Could Enable Server Code Execution
Critical Next.js vulnerability CVE-2026-94545, rated CVSS 9.5, could allow unauthenticated remote code execution through crafted input passed to Node.js ImageResponse.
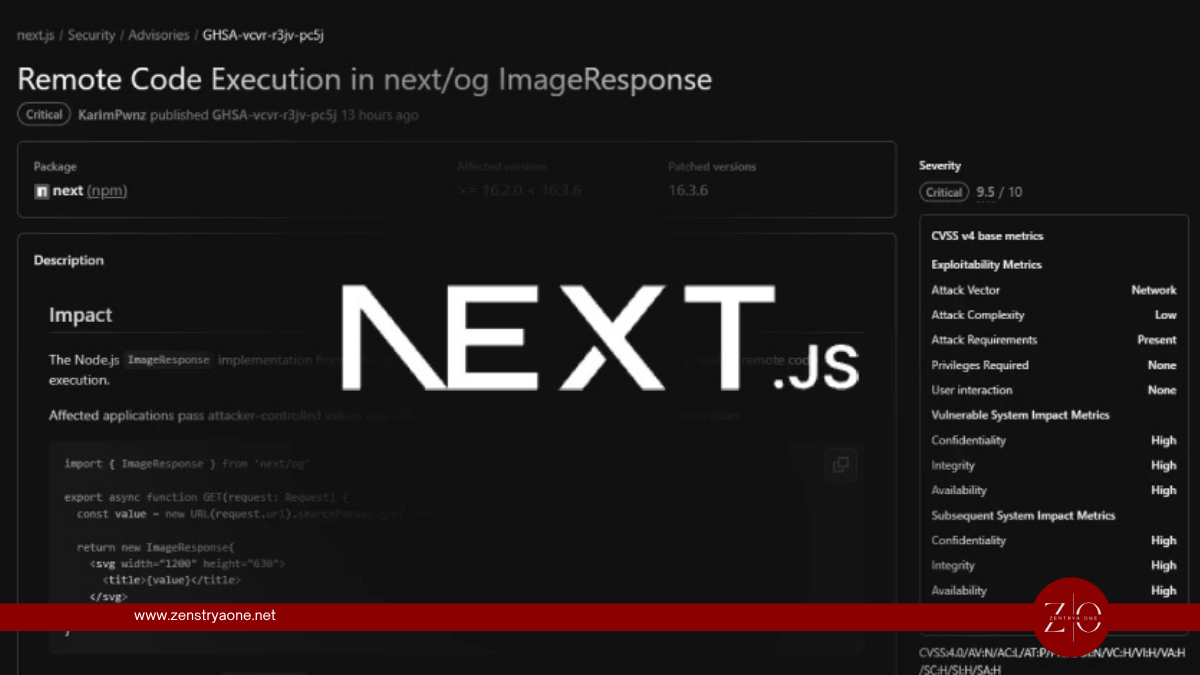
A critical security vulnerability in Next.js could allow unauthenticated attackers to achieve remote code execution (RCE) on vulnerable servers by supplying specially crafted input during image generation.
Tracked as CVE-2026-94545, the flaw affects the Node.js implementation of ImageResponse from next/og and carries a CVSS 4.0 score of 9.5. Vercel patched the vulnerability in Next.js 16.3.6.
CVE-2026-94545 at a Glance
| Detail | Information |
|---|---|
| CVE | CVE-2026-94545 |
| Severity | Critical |
| CVSS | 9.5 |
| Affected Versions | Next.js 16.2.0 – 16.3.5 |
| Fixed Version | Next.js 16.3.6 |
| Component | Node.js ImageResponse (next/og) |
| Authentication | Not required |
| Potential Impact | Remote Code Execution |
| Active Exploitation | None publicly reported |
The Edge implementation of ImageResponse is not affected, and Next.js 15 is also outside the affected version range.
How the Vulnerability Works
Next.js applications commonly use ImageResponse to dynamically generate Open Graph images, social-media previews, and other server-rendered images.
Internally, ImageResponse uses Vercel's Satori library to convert layouts into SVG before producing the final image.
The vulnerability becomes exploitable when an application passes attacker-controlled values into SVG content, attributes, or styles while using the Node.js ImageResponse implementation. Certain values were not properly escaped by Satori, allowing malicious input to be interpreted as SVG markup instead of ordinary text.
The attack path can be summarized as:
Attacker-Controlled Input → ImageResponse → Satori SVG Generation → Crafted SVG Content → Vulnerable Dependency Processing → Potential Server RCE
No authentication or user interaction is required, although the application must use ImageResponse in a vulnerable manner.
Not Every Next.js Application Is Vulnerable
Running an affected Next.js version alone does not automatically make an application exploitable.
The vulnerable scenario requires:
- Next.js 16.2.0 through 16.3.5
- Node.js
ImageResponsefromnext/og - Attacker-controlled values reaching SVG content, attributes, or styles
Applications using the Edge implementation or applications that never pass untrusted input into ImageResponse are not affected by this specific attack.
Satori Also Patched
The underlying flaw exists in Satori, where certain attacker-controlled values could reach generated SVG output without proper escaping.
Developers using Satori directly should upgrade to Satori 0.33.5 or later. Interestingly, Satori's own advisory rates the underlying issue as Moderate, while Vercel rates its impact through Next.js as Critical because the downstream processing can potentially result in server-side code execution.
What Developers Should Do
Next.js developers should upgrade immediately to:
Next.js 16.3.6
Applications on the 16.2 branch should move to 16.3.6 because no separate patched 16.2 release was available at disclosure.
If an immediate upgrade is impossible, Vercel recommends preventing all attacker-controlled data from reaching SVG content, attributes, or styles rendered through the Node.js ImageResponse implementation.
Developers should search their projects for:
import { ImageResponse } from 'next/og'
and review route handlers and opengraph-image implementations for untrusted input.
No Active Exploitation Reported
As of September 23, 2026, there were no public reports of CVE-2026-94545 being exploited in the wild and no public exploit code had been identified.
However, because exploitation is network-accessible, requires no authentication, and could potentially provide server-side code execution, affected applications should be updated without delay.
Security Takeaway
CVE-2026-94545 highlights the security risks created when untrusted user input reaches server-side image-generation pipelines.
The key attack scenario is:
Malicious Input → SVG Injection → Image Processing → Potential Server Code Execution
Organizations using Next.js 16.2 or 16.3 should identify applications using next/og ImageResponse, determine whether attacker-controlled input reaches SVG generation, and upgrade affected deployments to Next.js 16.3.6.
Related reporting
Weekly Cybersecurity Recap: Atlassian Exploits, Helpdesk Zero-Days, Rogue Certificates and ShinyHunters Arrests
Weekly cybersecurity recap covering Atlassian CVE-2026-21589 exploitation, Zammad zero-days, ShinyHunters arrests, rogue Google certificates, DarkSword malware and emerging AI security threats.
Hackers Begin Exploiting Critical Atlassian Data Center Flaw Within Hours of Disclosure
Hackers begin exploiting critical Atlassian Data Center vulnerability CVE-2026-21589 within hours of disclosure. Eight products affected, with patches available.
Anthropic Expands Claude Access for Cybersecurity Teams After Discovering 129,000 Software Vulnerabilities
Anthropic expands Claude AI access for cybersecurity teams after Project Glasswing identifies over 129,000 verified software vulnerabilities, including thousands of critical and high-severity flaws.