The Wire
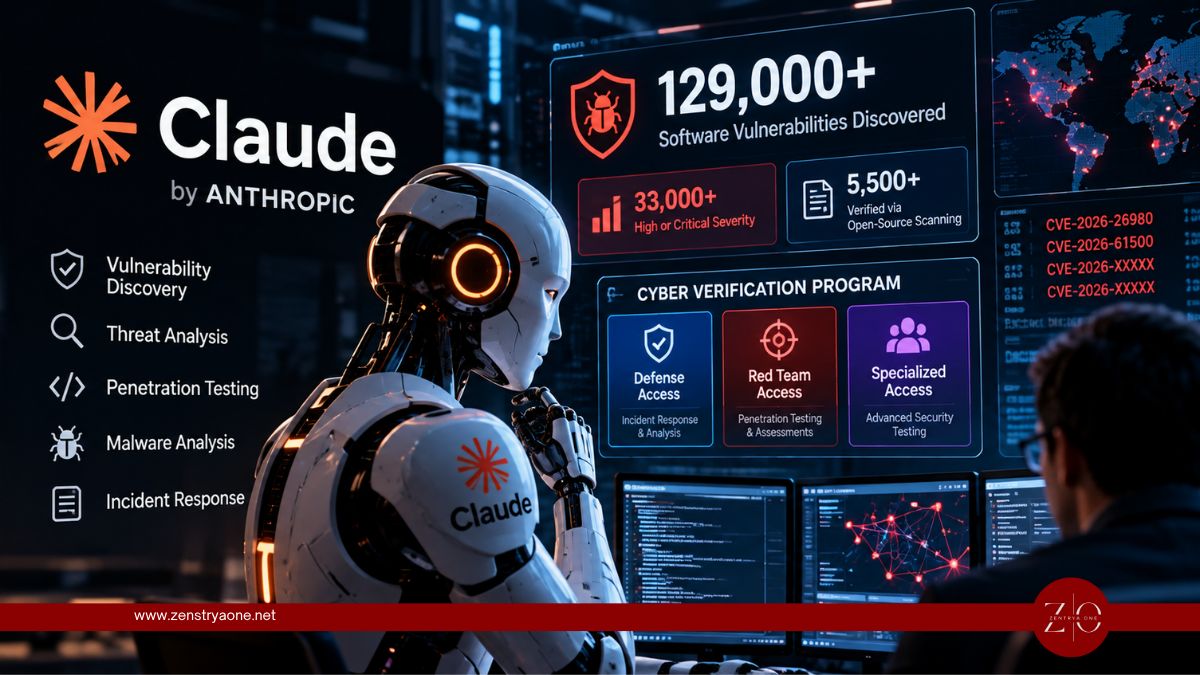
FILEDWeekly Cybersecurity Recap: Atlassian Exploits, Helpdesk Zero-Days, Rogue Certificates and ShinyHunters Arrests CRITICALHackers Begin Exploiting Critical Atlassian Data Center Flaw Within Hours of Disclosure CRITICALAnthropic Expands Claude Access for Cybersecurity Teams After Discovering 129,000 Software Vulnerabilities FILEDOver 100 Compromised Websites Spread LunexStealer Through Fake Cloudflare Verification Pages CRITICALEY Data Breach Exposes Sensitive Information of Goldman Sachs and Man Group Clients CRITICALLibreOffice and OpenOffice Flaws Let Malicious Spreadsheets Execute Code Without Macro Warnings FILEDWikimedia Says ‘Rogue’ OpenAI Agents Tried to Exploit Tools and Generated Millions of Requests FILEDGoogle Pauses Open-Source Product Bug Bounties After Surge in Invalid Automated Reports FILEDWeekly Cybersecurity Recap: Atlassian Exploits, Helpdesk Zero-Days, Rogue Certificates and ShinyHunters Arrests CRITICALHackers Begin Exploiting Critical Atlassian Data Center Flaw Within Hours of Disclosure CRITICALAnthropic Expands Claude Access for Cybersecurity Teams After Discovering 129,000 Software Vulnerabilities FILEDOver 100 Compromised Websites Spread LunexStealer Through Fake Cloudflare Verification Pages CRITICALEY Data Breach Exposes Sensitive Information of Goldman Sachs and Man Group Clients CRITICALLibreOffice and OpenOffice Flaws Let Malicious Spreadsheets Execute Code Without Macro Warnings FILEDWikimedia Says ‘Rogue’ OpenAI Agents Tried to Exploit Tools and Generated Millions of Requests FILEDGoogle Pauses Open-Source Product Bug Bounties After Surge in Invalid Automated Reports
CyberNews by Zentrya One
Tag

Artificial Intelligence

Every report filed under this tag.

Cloud & AppSec

Claude Used to Automate Exploitation and Data Theft Across Multiple Victims

Cybercriminals and state-sponsored threat actors are increasingly using artificial intelligence to automate portions of real-world cyberattacks, with Anthropic revealing that its Claude models were incorporated into multi-stage operations involving reconnaissance, exploitation, credential theft and data exfiltration.

critical Cloud & AppSec

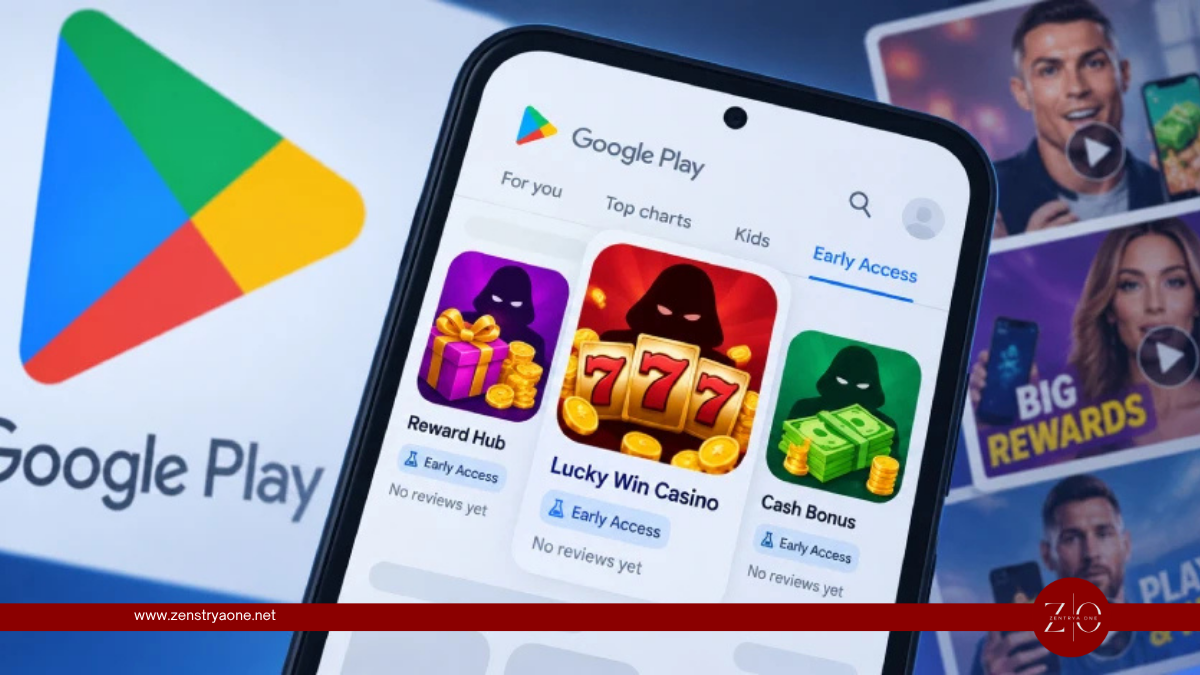
Google Play Early Access Abused to Distribute Thousands of Deceptive Android Apps

Cybercriminals are exploiting Google Play's Early Access program to distribute deceptive Android applications, including fake gambling platforms, financial scams, game clones and potentially malicious utilities, while taking advantage of the lack of public ratings and reviews.

critical CVE-2026-59821 Cloud & AppSec

Nearly 10% of Exposed LiteLLM Gateways Still Accepted the Default Admin Key

Security researchers have discovered that nearly one in ten publicly accessible LiteLLM deployments were either using the platform's default administrative key or operating without authentication, potentially exposing AI infrastructure to serious attacks.

The Daily Brief

Stay informed. Stay prepared. Stay one step ahead.

One brief each morning: the advisories that matter, the noise removed.

Double opt-in. One-click unsubscribe in every email. We never sell addresses.