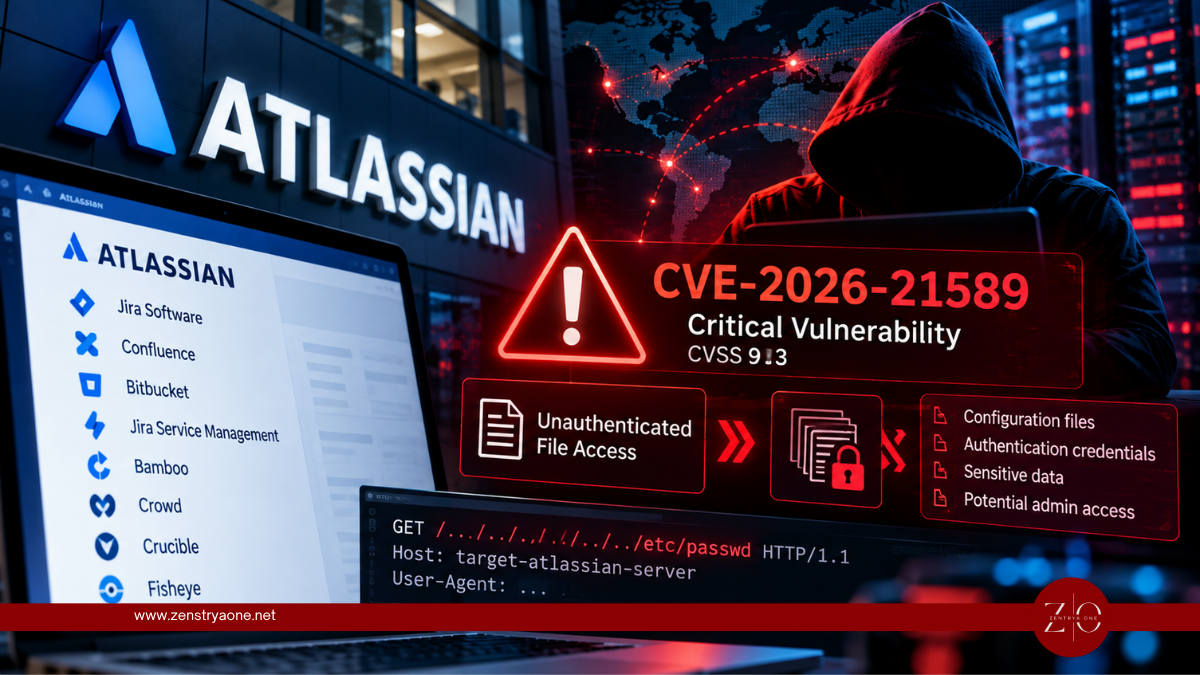
Hackers Begin Exploiting Critical Atlassian Data Center Flaw Within Hours of Disclosure
Hackers begin exploiting critical Atlassian Data Center vulnerability CVE-2026-21589 within hours of disclosure. Eight products affected, with patches available.
Every report filed under this tag.
Hackers begin exploiting critical Atlassian Data Center vulnerability CVE-2026-21589 within hours of disclosure. Eight products affected, with patches available.
Anthropic expands Claude AI access for cybersecurity teams after Project Glasswing identifies over 129,000 verified software vulnerabilities, including thousands of critical and high-severity flaws.
Critical LibreOffice and Apache OpenOffice vulnerabilities allow malicious spreadsheets to execute Java code without macro warnings. LibreOffice users should update, while OpenOffice users should disable Java until a fix is released.
Google pauses product vulnerability submissions to its OSS bug bounty program after a surge in invalid automated reports, while supply-chain reports and existing submissions remain unaffected.
Atlassian patches CVE-2026-21589, a critical CVSS 9.3 flaw allowing unauthenticated attackers to access known files across Jira, Confluence, Bitbucket and five other Data Center products.
Microsoft patches CVE-2026-96940, a high-severity Exchange Server flaw that could let authenticated attackers access other users' mailboxes, emails and attachments.
Apple plans stronger macOS Full Disk Access controls as increasingly autonomous AI agents raise concerns about access to files, emails, messages, browsing history and other sensitive user data.
Warlock ransomware attackers exploit Microsoft SharePoint vulnerabilities to gain initial access, disable security tools and distribute ransomware across critical infrastructure networks.
A public PoC for Apple CoreGraphics CVE-2026-86950 demonstrates memory corruption through a malicious PDF, while new WhatsApp PDF protections raise questions about a possible delivery path.
Kiteworks patched a previously unknown critical vulnerability discovered during a nine-hour precautionary shutdown prompted by intelligence about a potential cyberattack, with no evidence of exploitation.
Attackers are actively exploiting WordPress CVE-2026-87902, a critical CVSS 9.2 flaw that enables unauthenticated local PHP file inclusion and conditional remote code execution.
MikroTrick chains CVE-2026-67279 and CVE-2026-86060 to let attackers take full control of internet-exposed MikroTik RouterOS devices without a password or SSH key.
One brief each morning: the advisories that matter, the noise removed.
Double opt-in. One-click unsubscribe in every email. We never sell addresses.
Subscribe for walkthroughs and security tips.